vlt is open to everyone: a free npm registry, no account, no token
vlt now serves the public npm registry to anyone: no sign-up, no token, one flag. Point npm, pnpm, yarn, bun or deno at it, and vlt already uses it by default.
- Author
- Published
tl;dr: vlt is open to everyone
- vlt is now offering a public npm mirror registry, free for anyone.
- No account, no token, no auth line. Usage limits apply.
- Works with npm, pnpm, yarn, bun and deno. vlt already uses it by default.
- Faster than npm.
What changed
Until now, installing from vlt's npm mirror meant signing up for a vlt.io account, creating a token and adding an auth line to .npmrc (or equivalent config).
vlt itself shipped with no default registry, so on a fresh machine vlt install stopped with Missing registry configuration until you ran vlt setup.
Now the mirror is open to everyone. 🎉
via GIPHY
Since vlt v1.8.0, the mirror is vlt's default registry: install vlt, run vlt install, done. Nothing to configure.
Using npm, pnpm, yarn, bun or deno?
Here's how our CEO Darcy put it:
Pick your package manager, set a registry configuration, and install.
Darcy's flags example are great for a quick try but to use the mirror consistently on every install in a given project, set it as project config:
Public npm mirror
# Use the vlt npm mirror
npm config set registry https://registry.vlt.io/upstream/npm/ --location=project# vlt uses the vlt npm mirror by default (vlt)# Use the vlt npm mirror (npm)
npm config set registry https://registry.vlt.io/upstream/npm/ --location=project# Use the vlt npm mirror (pnpm)
pnpm config set registry https://registry.vlt.io/upstream/npm/ --location=project# Use the vlt npm mirror (yarn)
yarn config set npmRegistryServer "https://registry.vlt.io/upstream/npm/"# Add to your .npmrc (deno)
registry=https://registry.vlt.io/upstream/npm/# Add to your bunfig.toml (bun)
[install]
registry = "https://registry.vlt.io/upstream/npm/"# Install, no login or token
$npm install
Wondering what to do with your existing lockfile? The public mirror docs cover it, along with everything else the mirror serves.
Your stale tokens can't break it
The mirror ignores credentials. Our edge strips the Authorization header from every request to the public mirror, so every caller gets the same response. An expired or revoked token sitting in .npmrc or your keychain will never turn an install into a 401. That's one less secret to manage in CI, and one less thing to debug when a pipeline goes red.
Bonus: it's fast
It's currently faster than npm at installing the same dependencies with the same npm client:
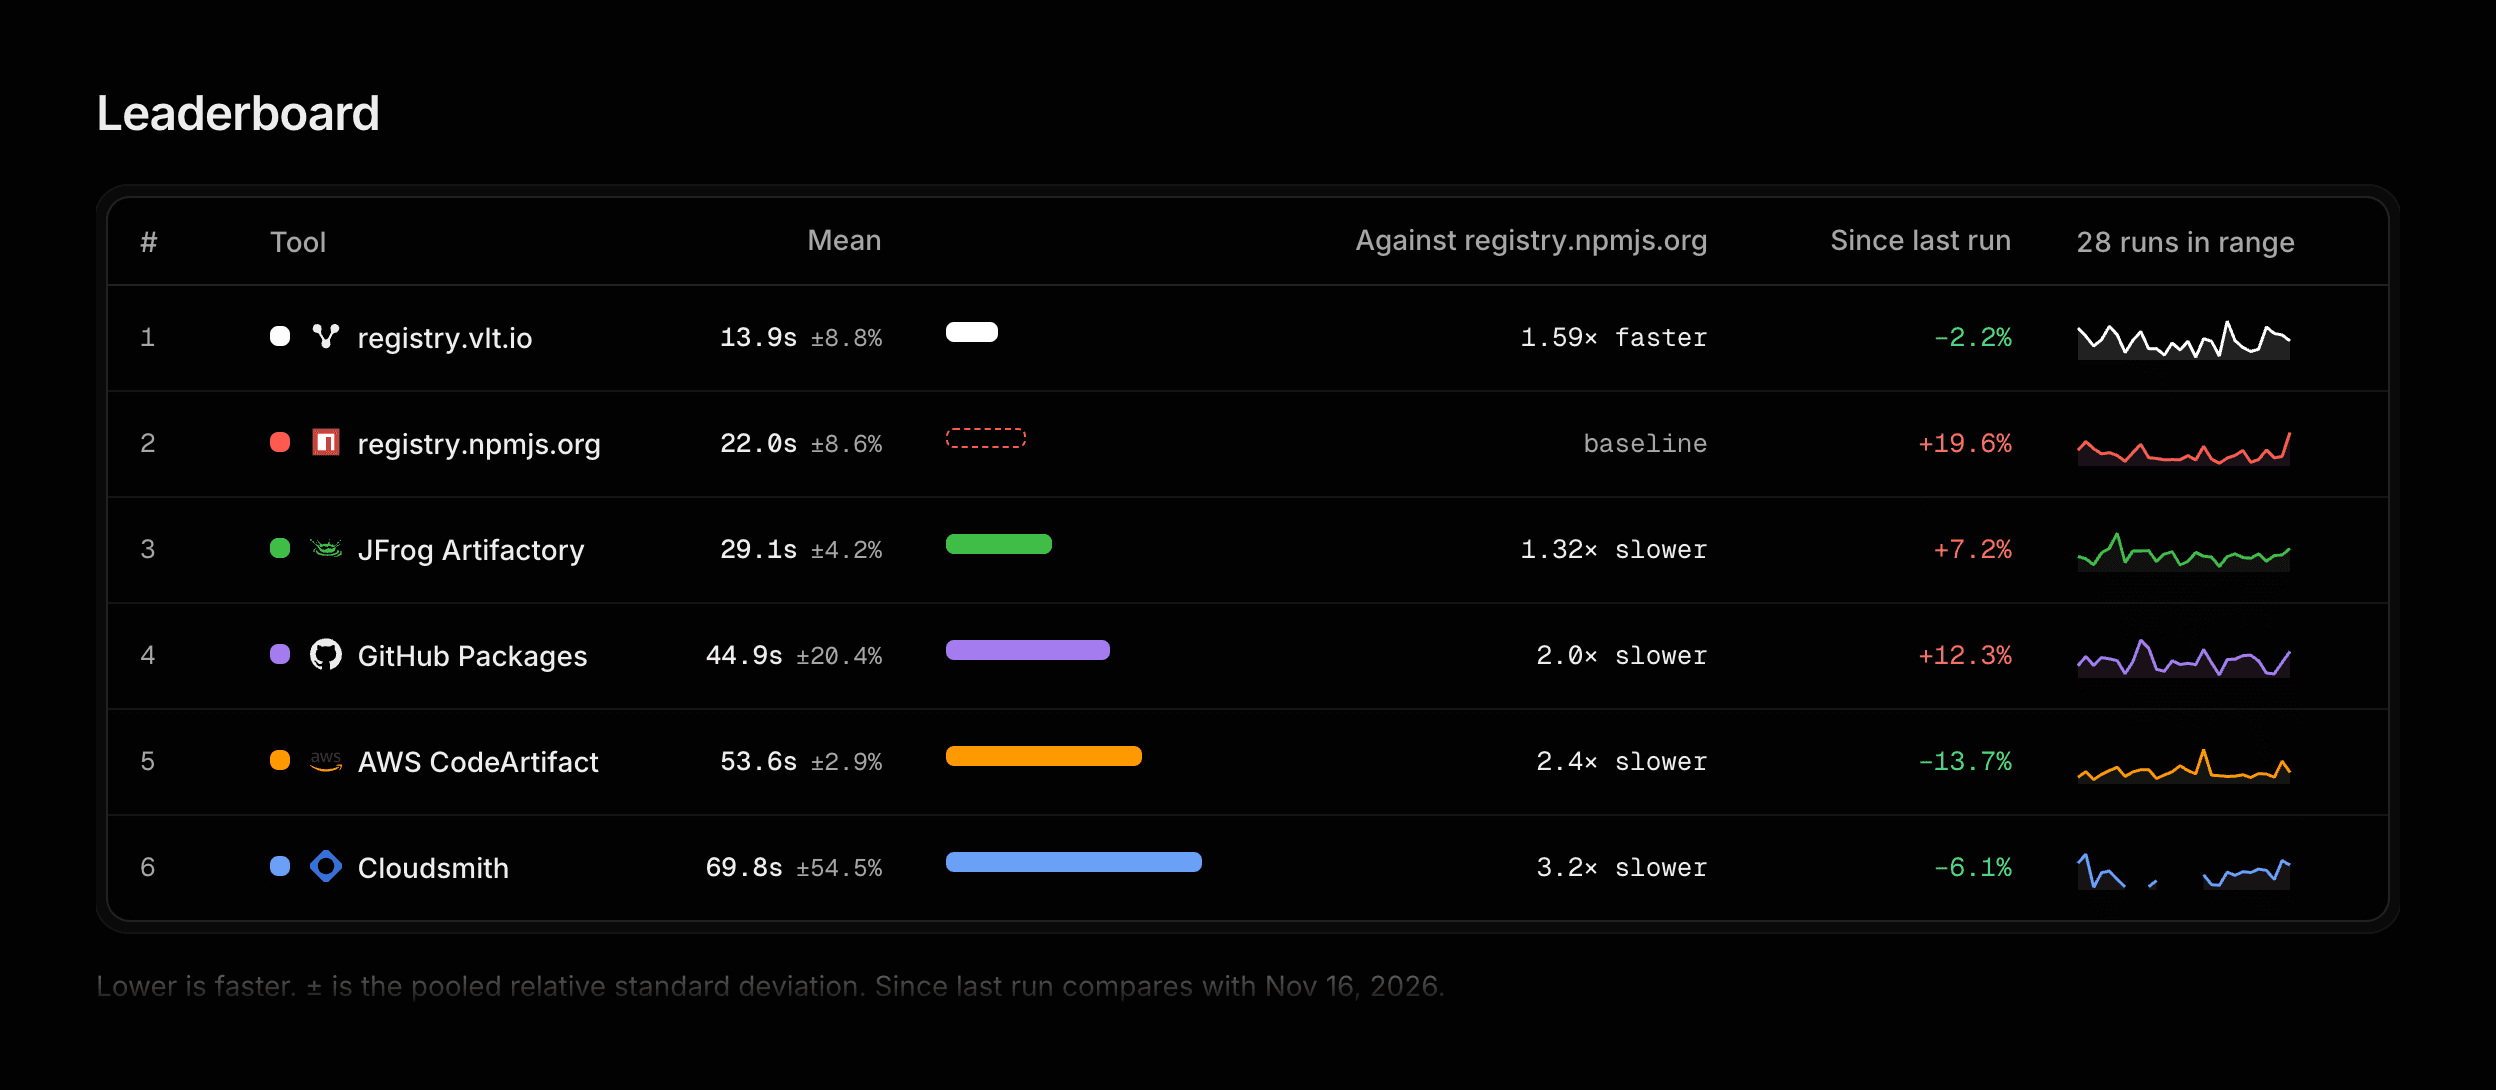
The benchmarks run every night, so the table above is a snapshot from November 17, 2026. See the registry leaderboard for the latest numbers.
Fair use
The public mirror is free for everyone, and we want to keep it that way. Use it for your projects, your CI and your experiments. It's a shared, free service with usage limits.
Thank you
A huge thank you to all our contributors and engineers who made this happen. Opening the mirror to everyone is a big deal for the JavaScript packaging ecosystem, and it's only the start: we'll keep pushing for a faster, more secure way to consume and publish npm packages.
Get new posts by email
Deep dives and product updates from the vlt team.
